
Sounds like an opportunity for a tool that fakes such things.
Or, just don’t use the garbage apps that require this?
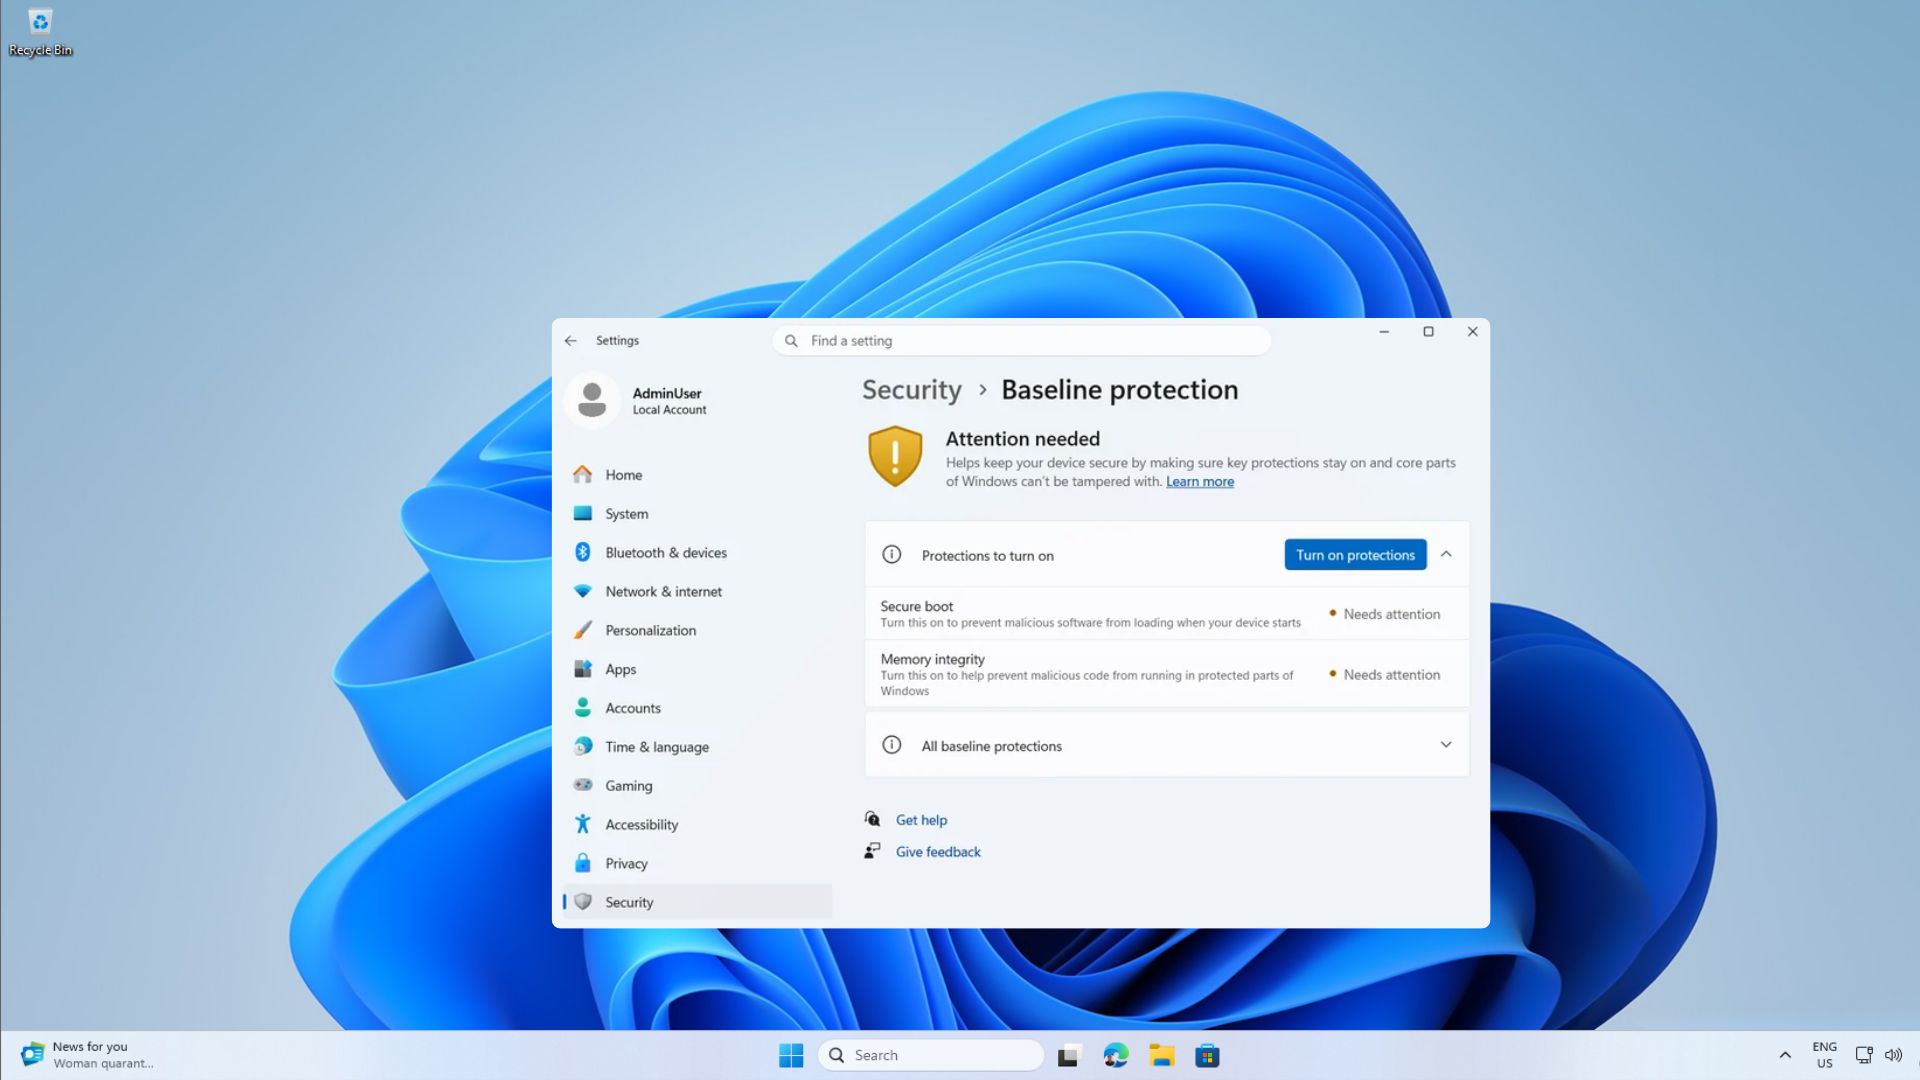
Also, this is where the average user will finally see the objectives of secure boot for Windows - it’s to get a phone-like locked-down environment.
There are places where this is useful, say enterprise environments where it’s arguably necessary. But for the average user it’s just pushing towards you not owning the device in front of you.
I just don’t understand why Microsoft does not default to opt-in.
Like, that would be the easiest thing they could do to garner the most good will.
All they would have to do would be to say, “Hey, we are now offering this feature, you can use it if you want to, if you don’t, you don’t have to do anything.”
Literally, if I had the death note, every Microsoft executive would be in it right now, and every new executive right along with them until they hired people who understood consent.
Applocker is already a thing since Windows 7, opt-in.
This what they now are proposing is purely to restrict users
When you license your operating system, your computer is not yours.
For those that didn’t read the story. It’s not Windows that would block apps. It’s the app author in control on this.
We don’t like Linux running our programs. Well make a comparability layer to make our os special. 🙄

